Trust isn’t a soft extra that gets added once a product has found its audience. It’s part of the product itself.
For a startup, that can sound like a lot to take on. You’re trying to make something useful, keep it fast, explain it clearly and give people a reason to return. Yet the organisations that earn lasting confidence tend to see trust as a series of practical design decisions: what information is shown, what data is collected, how payments work, and whether a person can stay in control without hunting through a help centre.
Regulated digital entertainment offers a particularly useful lens. It operates with high expectations around identity, transparency, security and user protections. Not every startup faces the same rules, of course, but the underlying lessons travel well. Whether you’re building a subscription service, marketplace, health platform or productivity tool, people want to know what they’re agreeing to and what happens next.
Trust starts before someone creates an account
A first visit is often a quiet assessment. Does the service explain itself plainly? Are the key actions obvious? Does the page feel considered on a small screen, rather than merely squeezed into one?
Users rarely separate these details in their minds. A confusing sign-up flow, a broken button or vague wording can all create the same impression: this business may not have thought things through. That’s harsh, perhaps, but it’s human.
Good trust design removes needless uncertainty. It gives people answers at the point they need them, rather than making them guess.
That means:
-
saying what the product does in ordinary language;
-
showing important conditions before a commitment is made;
-
making prices, renewal terms and cancellation routes easy to find;
-
explaining why personal information is requested;
-
offering help that feels reachable when something goes wrong.
The point isn’t to make every screen wordy. Quite the opposite. Clear interfaces respect a person’s time. If you’ve ever abandoned a form because it asked for something without explanation, you’ll know why that matters.
Build around real journeys, not internal departments
Founders often know their product inside out. New users don’t. They arrive with a goal, a device, varying confidence with technology and, quite possibly, only a few minutes to spare.
That’s why user-centred design is more than usability testing at the end of a build. It begins with mapping the journey from the outside in. What does someone need to understand before registering? Where might they hesitate? What happens if they make an error, lose connectivity or need to alter a decision later?
Mobile performance is a promise
Mobile is where vague design decisions become obvious. A page that feels fine on a wide office monitor can become awkward when viewed one-handed on a phone with an imperfect connection.
For startups, mobile performance deserves product-level attention:
-
Keep key pages light. Large, unnecessary files slow down access and can make a service appear unreliable.
-
Prioritise the main task. A user should be able to register, browse, get support or manage settings without wrestling with pop-ups and clutter.
-
Use touch-friendly controls. Small links and tightly packed fields cause avoidable mistakes.
-
Design for interruptions. Save progress where appropriate, make error messages specific and allow a person to return without beginning again.
-
Test with real devices. Emulators are helpful, but they won’t fully show how a journey feels on a commuter train or in a patchy signal area.
Speed matters, but so does consistency. If a button says “Continue”, it should continue. If an account setting says it has been saved, that change needs to be reflected everywhere it matters.
Plain language earns more confidence than clever copy
There’s a temptation to soften difficult information with polished language. Usually, this backfires. People can spot when wording is trying to guide them around an important detail.
Say what will happen. Say when it will happen. Say what options are available.
For instance, “We’ll use your email address to send account security alerts” is clearer than “We may contact you with relevant service communications.” The first sentence lets someone make an informed choice. The second raises questions.
This applies to error messages, too. “We couldn’t verify that detail. Check it and try again, or contact support” is kinder and more useful than a red warning icon with “Invalid input”.
Resilience is what users notice when things go wrong
Trust is tested most firmly at moments of friction: a payment doesn’t complete, an account is locked, a page fails to load or a person wants to delete information.
A resilient platform doesn’t pretend these moments never happen. It plans for them.
The UK’s National Cyber Security Centre guidance is a sensible starting point for startups looking to turn security from an afterthought into an operating habit. That includes managing access carefully, keeping systems updated, monitoring for unusual activity and having a workable response plan.
Security should be visible, but not theatrical
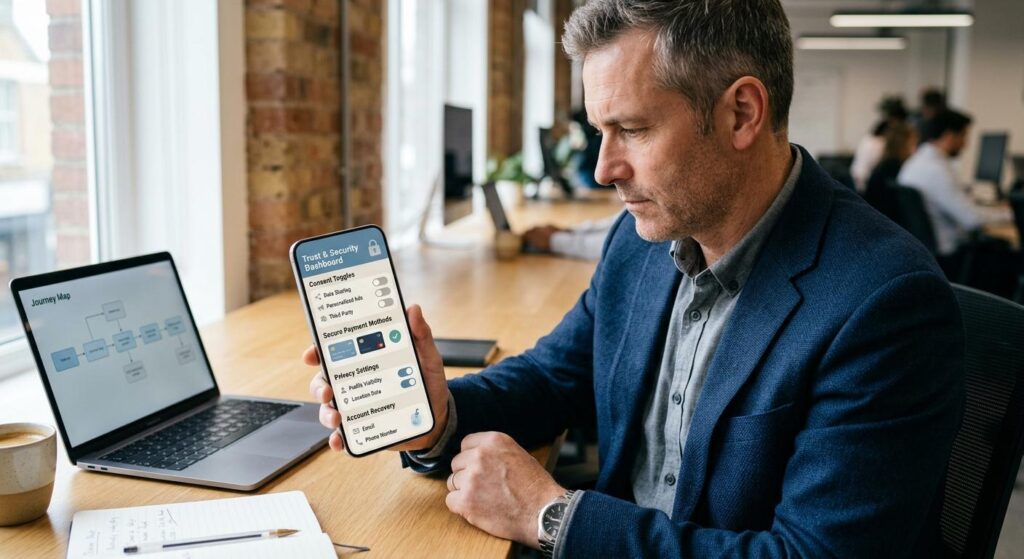
Security signals can reassure users, but only when they reflect something real. A padlock graphic on its own means little. More meaningful signals include:
-
clear account recovery processes;
-
multi-factor authentication where the risk warrants it;
-
alerts when important account details change;
-
recognisable payment steps;
-
timely, understandable updates if a service interruption occurs.
There’s a balance to strike. Too many prompts can become frustrating, while too few leave people unsure whether their account is protected. The right approach is risk-based: apply stronger checks around sensitive actions, explain why they are needed and keep the process proportionate.
Privacy-by-design means collecting less, with purpose
Privacy isn’t just a legal document tucked into a footer. It’s a question that should arise whenever a new feature is proposed: do we actually need this information, for this stated reason, for this long?
The concept of privacy-by-design is built around making privacy a default consideration throughout engineering and service design. The ICO’s guidance for organisations provides a useful UK reference point, especially for teams handling personal data.
In practice, that might mean separating optional profile fields from essential account details, limiting staff access to sensitive records and setting deletion or retention rules early. It also means avoiding consent screens that make one option glaringly easy and another needlessly difficult.
People should be able to understand:
-
what information is being collected;
-
why it is needed;
-
who it is shared with;
-
how they can change their choices;
-
how they can ask for help or raise a concern.
That’s not simply a compliance exercise. It can reduce support queries, prevent awkward surprises and encourage more considered product decisions.
Payment architecture needs calm, clear handling
Where money moves through a platform, ambiguity has no place. Users need confirmation of what they have authorised, whether a payment has completed and what to do if something looks wrong.
A dependable payment journey should have clear status updates, sensible fraud controls and a record that users can access without effort. Avoid unexplained redirects and unclear labels. If a third-party payment provider is involved, say so plainly.
Behind the scenes, teams should think about failure states as carefully as successful transactions. What happens if a confirmation arrives late? How are duplicate requests prevented? Who investigates a disputed payment, and how quickly can a customer reach them?
It may not be the most glamorous part of product development, but it’s where confidence is often won or lost.
Governance should be built into the interface
Governance can sound like board meetings and policy documents. In a digital service, it also appears in the everyday controls people see.
A well-governed product makes the important things findable. It does not bury age requirements, terms, privacy choices or contact routes beneath layers of navigation. It treats transparency as a feature.
For high-consideration services, that should include prominent information about eligibility, clear consent choices and settings that users can revisit. If someone can turn on a notification, they should be able to turn it off without a treasure hunt. If a service makes a significant change, the explanation should be specific enough to be useful.
Age assurance deserves particular care. Where a product is for adults only, the boundary must be meaningful rather than a token tick-box. Identity and age checks should be explained respectfully, with a clear reason for the request and a secure process for handling the information.
Control mechanisms matter just as much. Account management, contact preferences, data requests and support routes ought to work when someone needs them, not only when the product is behaving perfectly.
A factual case study: regulated UK digital entertainment
Case study: UK-regulated adult entertainment services provide a practical, limited example of trust-led interface design. An adult-only category such as slots online Bally Casino can be assessed for whether it presents game information clearly, shows credible security cues, uses age assurance and provides responsible-play tools and routes to support. UK Gambling Commission licensees are subject to rules designed to keep gambling fairer and safer, including requirements that are relevant to customer information and protections, as set out in the Commission’s Licence Conditions and Codes of Practice.
The startup lesson is not to copy a regulated service’s appearance. It is to recognise the design discipline behind it. When a service carries greater responsibility, clarity and user control cannot be treated as optional screens added at the end.
Responsible use note: Gambling is for adults aged 18+ only. If gambling is no longer feeling manageable, support is available from GamCare.
Turn trust into a roadmap, not a slogan
Trust becomes useful when a team can build, test and measure it. A short implementation checklist can help keep it grounded.
-
Map one complete customer journey each quarter, including errors, cancellations and support.
-
Set plain-language standards for pricing, consent, account changes and data explanations.
-
Review data collection feature by feature, recording the purpose and retention period.
-
Test mobile journeys on real devices and slower connections.
-
Run security and incident exercises so the team knows who does what when a problem occurs.
-
Track trust signals, such as successful task completion, support contacts about confusion, account recovery time, payment failure resolution and settings changes.
The strongest digital businesses don’t ask users to take trust on faith. They demonstrate it in hundreds of small moments: a form that makes sense, a policy that says what it means, a payment confirmation that arrives when expected and a control that genuinely gives someone control.
That’s a useful standard for any startup to aim for.